
SSL Certificate Decoder vs OpenSSL: Which Should You Use?
Two tools, same certificate, different jobs
Both an online SSL decoder and OpenSSL read the same certificate file and can tell you the domain, issuer, and expiry. The difference is the workflow around them. One is a page you open; the other is a command you run. Each fits certain tasks better.
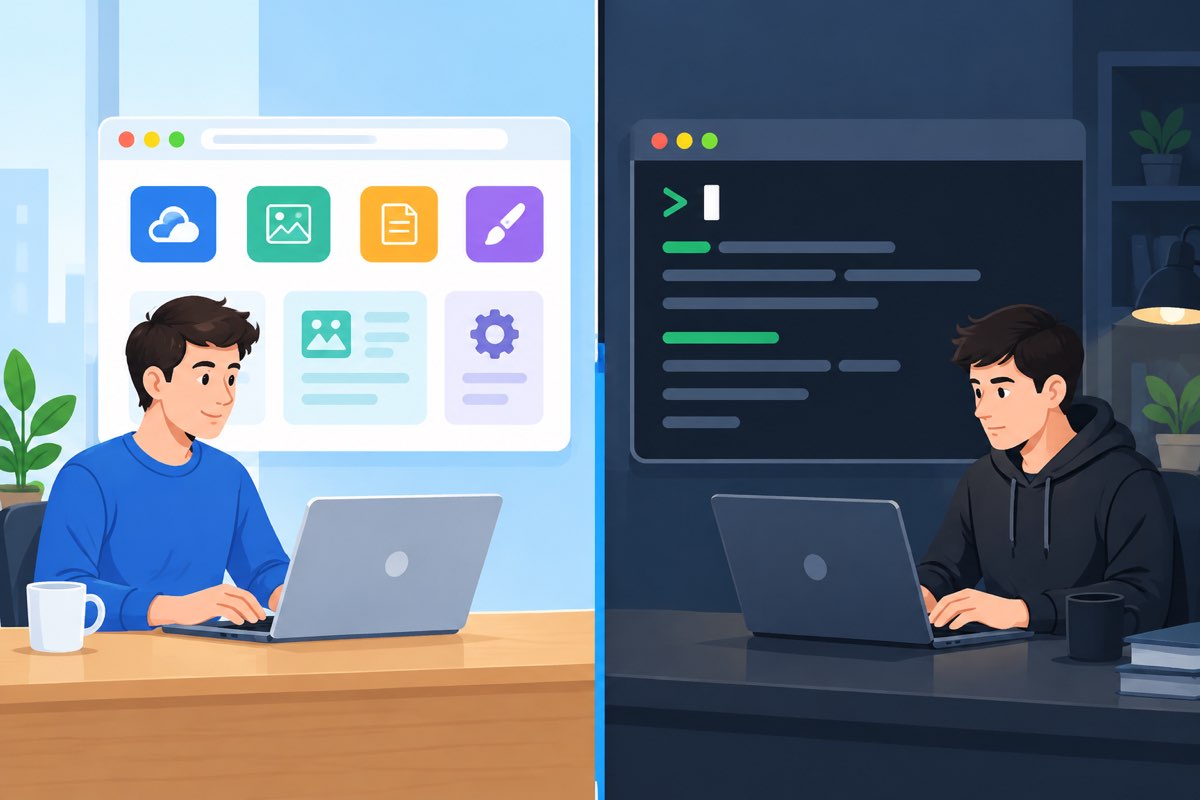
Side-by-side
| Dimension | Online SSL decoder | OpenSSL CLI |
|---|---|---|
| Setup | None — open the page | Install openssl, use a terminal |
| Speed for one check | Seconds, zero flags | Seconds, needs correct flags |
| Readable output | Formatted view with dates and SANs | Raw text; you filter with flags |
| Scripting / batch | Manual per domain | Loop over hosts in a shell script |
| Local files | No (needs a live host) | Yes — inspect a .crt/.pem directly |
| Audience | Non-technical, quick checks | DevOps, automation, deep inspection |
When each one wins
Reach for an online decoder when you need a fast answer: is this cert valid, who issued it, when does it expire — maybe on someone else's machine, with no terminal open. It's also the friendlier option for clients and colleagues who just want a screenshot.
Reach for OpenSSL when you're automating, checking dozens of hosts, or inspecting a local certificate file:
# check one remote host
echo | openssl s_client -connect example.com:443 2>/dev/null | openssl x509 -noout -subject -issuer -dates
# loop over a list of hosts
while read -r h; do
  echo "== $h"
  echo | timeout 10 openssl s_client -connect "$h:443" 2>/dev/null | openssl x509 -noout -enddate
done < hosts.txt
Bottom line
Keep both in your pocket. Use the decoder for quick human answers and sharing; use OpenSSL when the check needs to happen inside a script or against a file. They read the same certificate — they just fit different workflows.
FAQ
Which is faster for a one-off check?
The online decoder: type the domain, read the answer. OpenSSL demands a shell and the right flags.
Can OpenSSL do everything a web decoder does?
Yes, and more — but you need the binary and the syntax. The decoder's advantage is convenience, not coverage.
When should I use OpenSSL instead?
Any time the check is repeated, automated, or done on a local file.
Do they show the same expiry date?
Yes. Both read notBefore/notAfter from the identical certificate bytes.


