
What SSL Certificate Fields Matter Beyond Expiry Date?
An SSL certificate is more than a "valid until" date. Plenty of outages and browser warnings come from certificates that haven't expired at all. Here's what else to check, in plain terms.
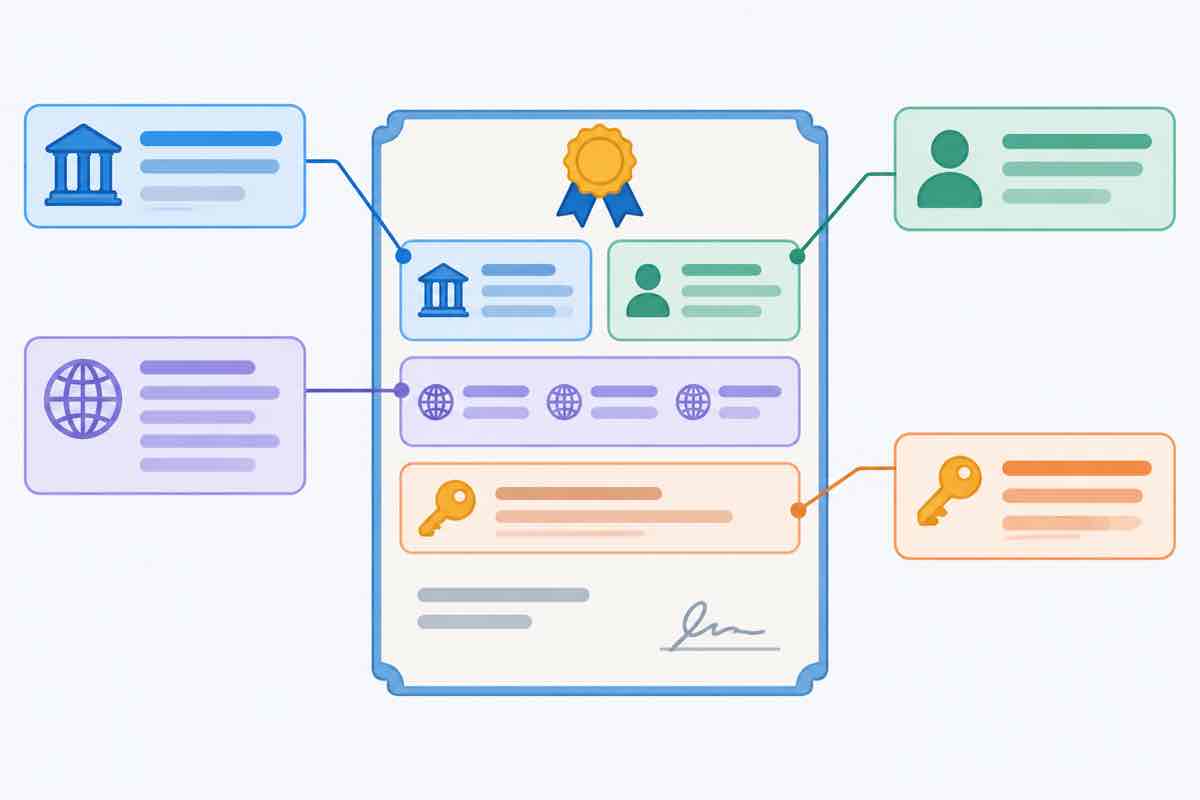
SSL certificate fields beyond expiry
Questions, answered
What fields matter beyond the expiry date?
The Subject Alternative Names, the issuer, the signature algorithm, the validity start, and the public key type and size all matter. A cert can be 'in date' and still be wrong.
What is the Subject Alternative Name, or SAN?
It's the actual list of hostnames the certificate covers. Modern browsers read the SAN, not the older common-name field, so a domain missing from the SAN fails even if the dates are fine.
What's the difference between issuer and subject?
The subject is who the certificate belongs to; the issuer is the certificate authority that signed it. If you don't recognize or trust the issuer, the certificate isn't trusted.
What does the signature algorithm tell me?
It shows how the CA signed the certificate. SHA-256 and stronger are normal today; SHA-1 is deprecated and triggers warnings regardless of the expiry date.
What's a notBefore problem?
A certificate has a start date too. If your device clock is wrong, or the cert was just issued and you're ahead of that time, it reads as not yet valid.
How do I actually read these fields?
Drop a PEM or a live host into an SSL certificate decoder, or run openssl s_client and openssl x509 on the command line to print the full text.
If you're troubleshooting a cert, check the SAN and issuer before assuming the date is the problem. Most "it should work" failures live there.


